Overview & AI Governance Architecture Business & Operational Significance 🎯 User Roles & Key Capabilities Visual Interface & Layout Field Reference & Tool Assignment Parameters SBC MCP Tool Catalog & Action Capabilities The Official System MCP Role Profiles Runtime Execution & Security Guard Mechanics Troubleshooting & Verification Model Context Protocol (MCP) AI Integration Glossary
In Ring2All SBC , the MCP Role Profiles module provides strict, zero-trust security governance over the artificial intelligence tools exposed by the Model Context Protocol (MCP) server. The platform’s integrated AI assistant (NOC Copilot ) interacts directly with running SIP Engine daemons, Media Relay proxies, and live routing tables to diagnose network faults, explain SIP ladder traces, provision carrier gateways, and adjust perimeter firewall states.
┌─────────────────────────────────────────────────┐
│ (user_id, assigned mcp_role_id) │
└────────────────────────┬────────────────────────┘
Prompt: "Unban IP 192.168.1.50"
┌─────────────────────────────────────────────────┐
│ Ring2All SBC NOC Copilot │
│ (LLM Engine / Claude) │
└────────────────────────┬────────────────────────┘
Formulates Tool Call Request:
{"tool": "unban_ip_address", "ip": "..."}
┌─────────────────────────────────────────────────┐
│ MCP Security Enforcement Guard │
│ (assertUserCanExecuteTool Check) │
└────────────────────────┬────────────────────────┘
┌───────────────────────┴───────────────────────┐
[Tool in allowed_tools] [Tool NOT in allowed_tools]
Invoke Engine JSON-RPC Reject Call Immediately
htable.delete ipban ... 403 Forbidden: Unauthorized
To eliminate the risk of prompt injection, unauthorized carrier tampering, or unintended dialplan reloading, every AI tool invocation (tools/call) is cryptographically and logically validated against the user’s assigned MCP Role Profile before executing.
Prompt Injection & Hallucination Containment : Guarantees that even if an external caller or malicious SIP header attempts prompt injection against the AI Copilot, the model cannot execute tools outside the user’s permitted profile.Controlled AI Autonomy in Mission-Critical Telecom : Allows Tier-1 technicians to use AI for diagnostic querying (e.g., inspecting SIP ladders and QoS metrics) while strictly withholding permission to alter carrier weights, provision wholesale trunks, or execute shell commands.Granular Segregation Between Diagnostics and Configuration : Separates read-only analytical tools (get_sip_traces, get_traffic_analytics) from state-modifying actions (reload_dispatchers, create_carrier, unban_ip_address).Compliance & AI Governance Auditing : Maintains an immutable evidentiary trail of all AI tool executions, recording the human operator on whose behalf the AI tool was called.
Role
Primary Use Case
Key Capabilities
AI Systems Architect Copilot Governance Policy
Define MCP tool profiles, structure tool catalogs, and enforce organizational AI boundaries.
NOC Director Safe Operational Acceleration
Empower support engineers with AI-assisted diagnostics while ensuring operational stability.
Security Operations Analyst AI Threat & Action Auditing
Review AI tool call logs, investigate blocked execution attempts, and audit unban actions.
SBC Telecom Engineer Conversational Telemetry Inspection
Utilize authorized tools to query real-time dispatcher health, analyze MOS scores, and isolate trunk faults.
AI Platform Copilot / Administration Agent Self-Introspection & AI Tool Boundary Verification
Inspect assigned tool permissions, verify AI role scopes, and ensure compliant execution within authorized telephony boundaries.
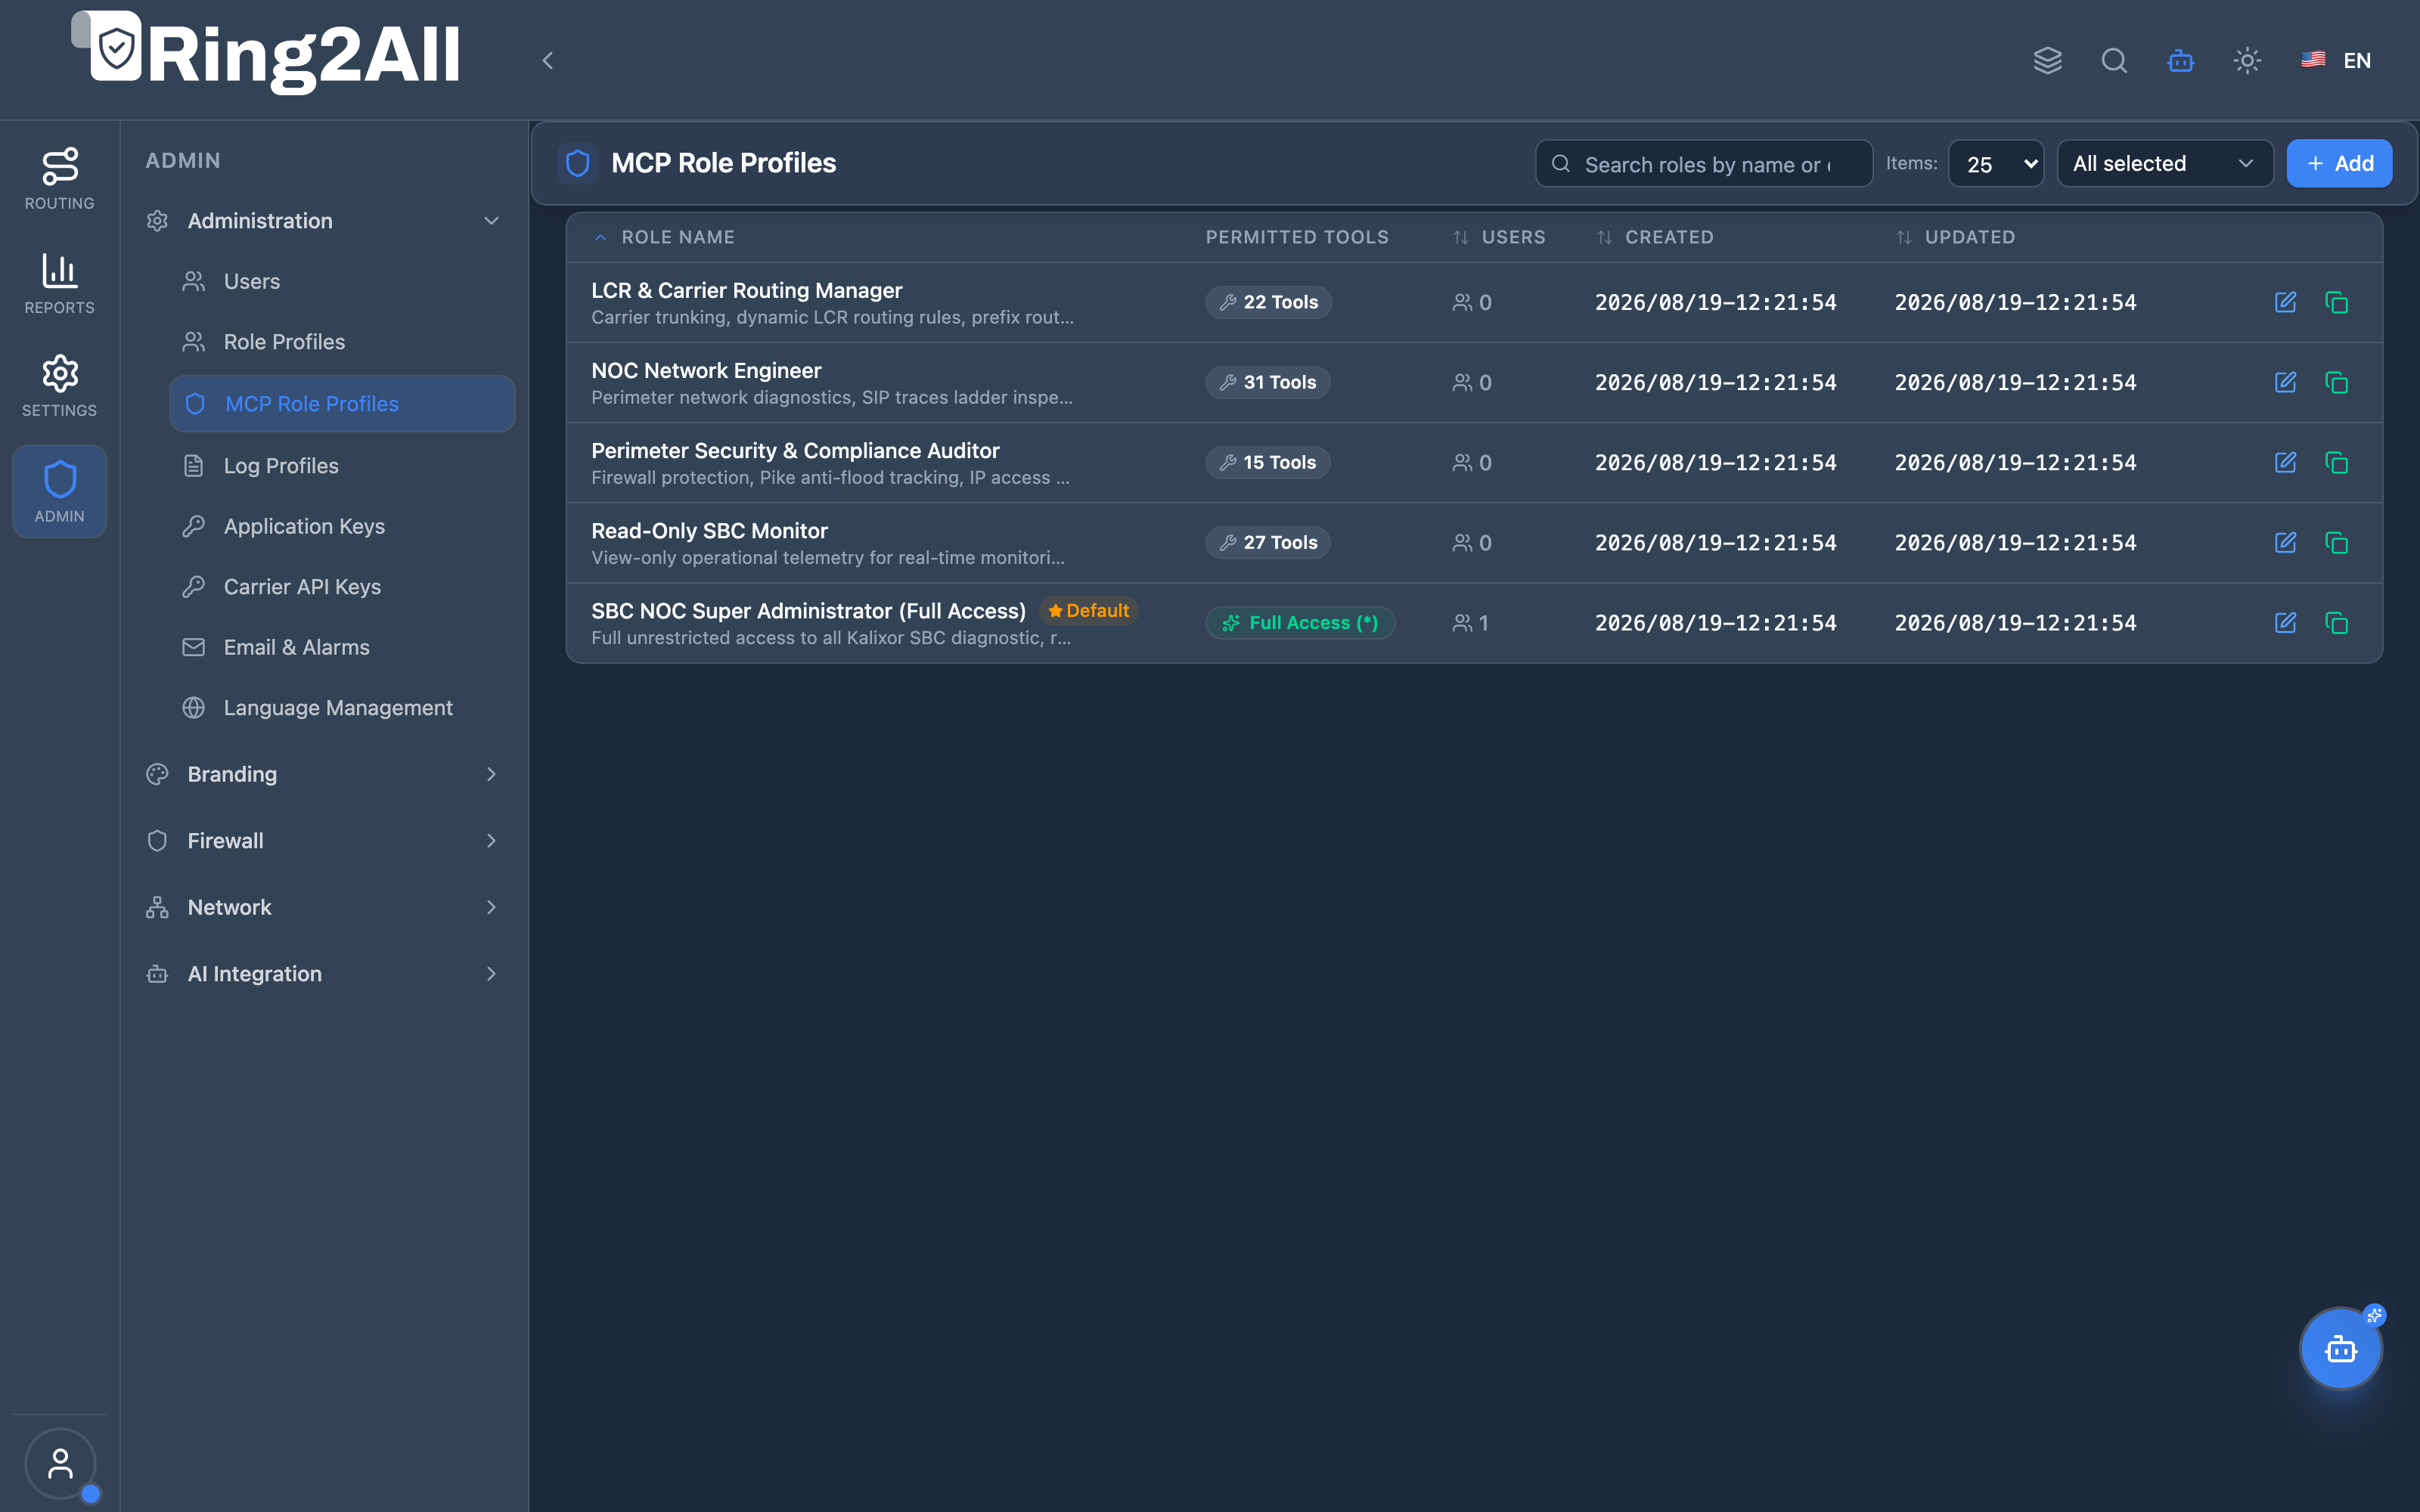
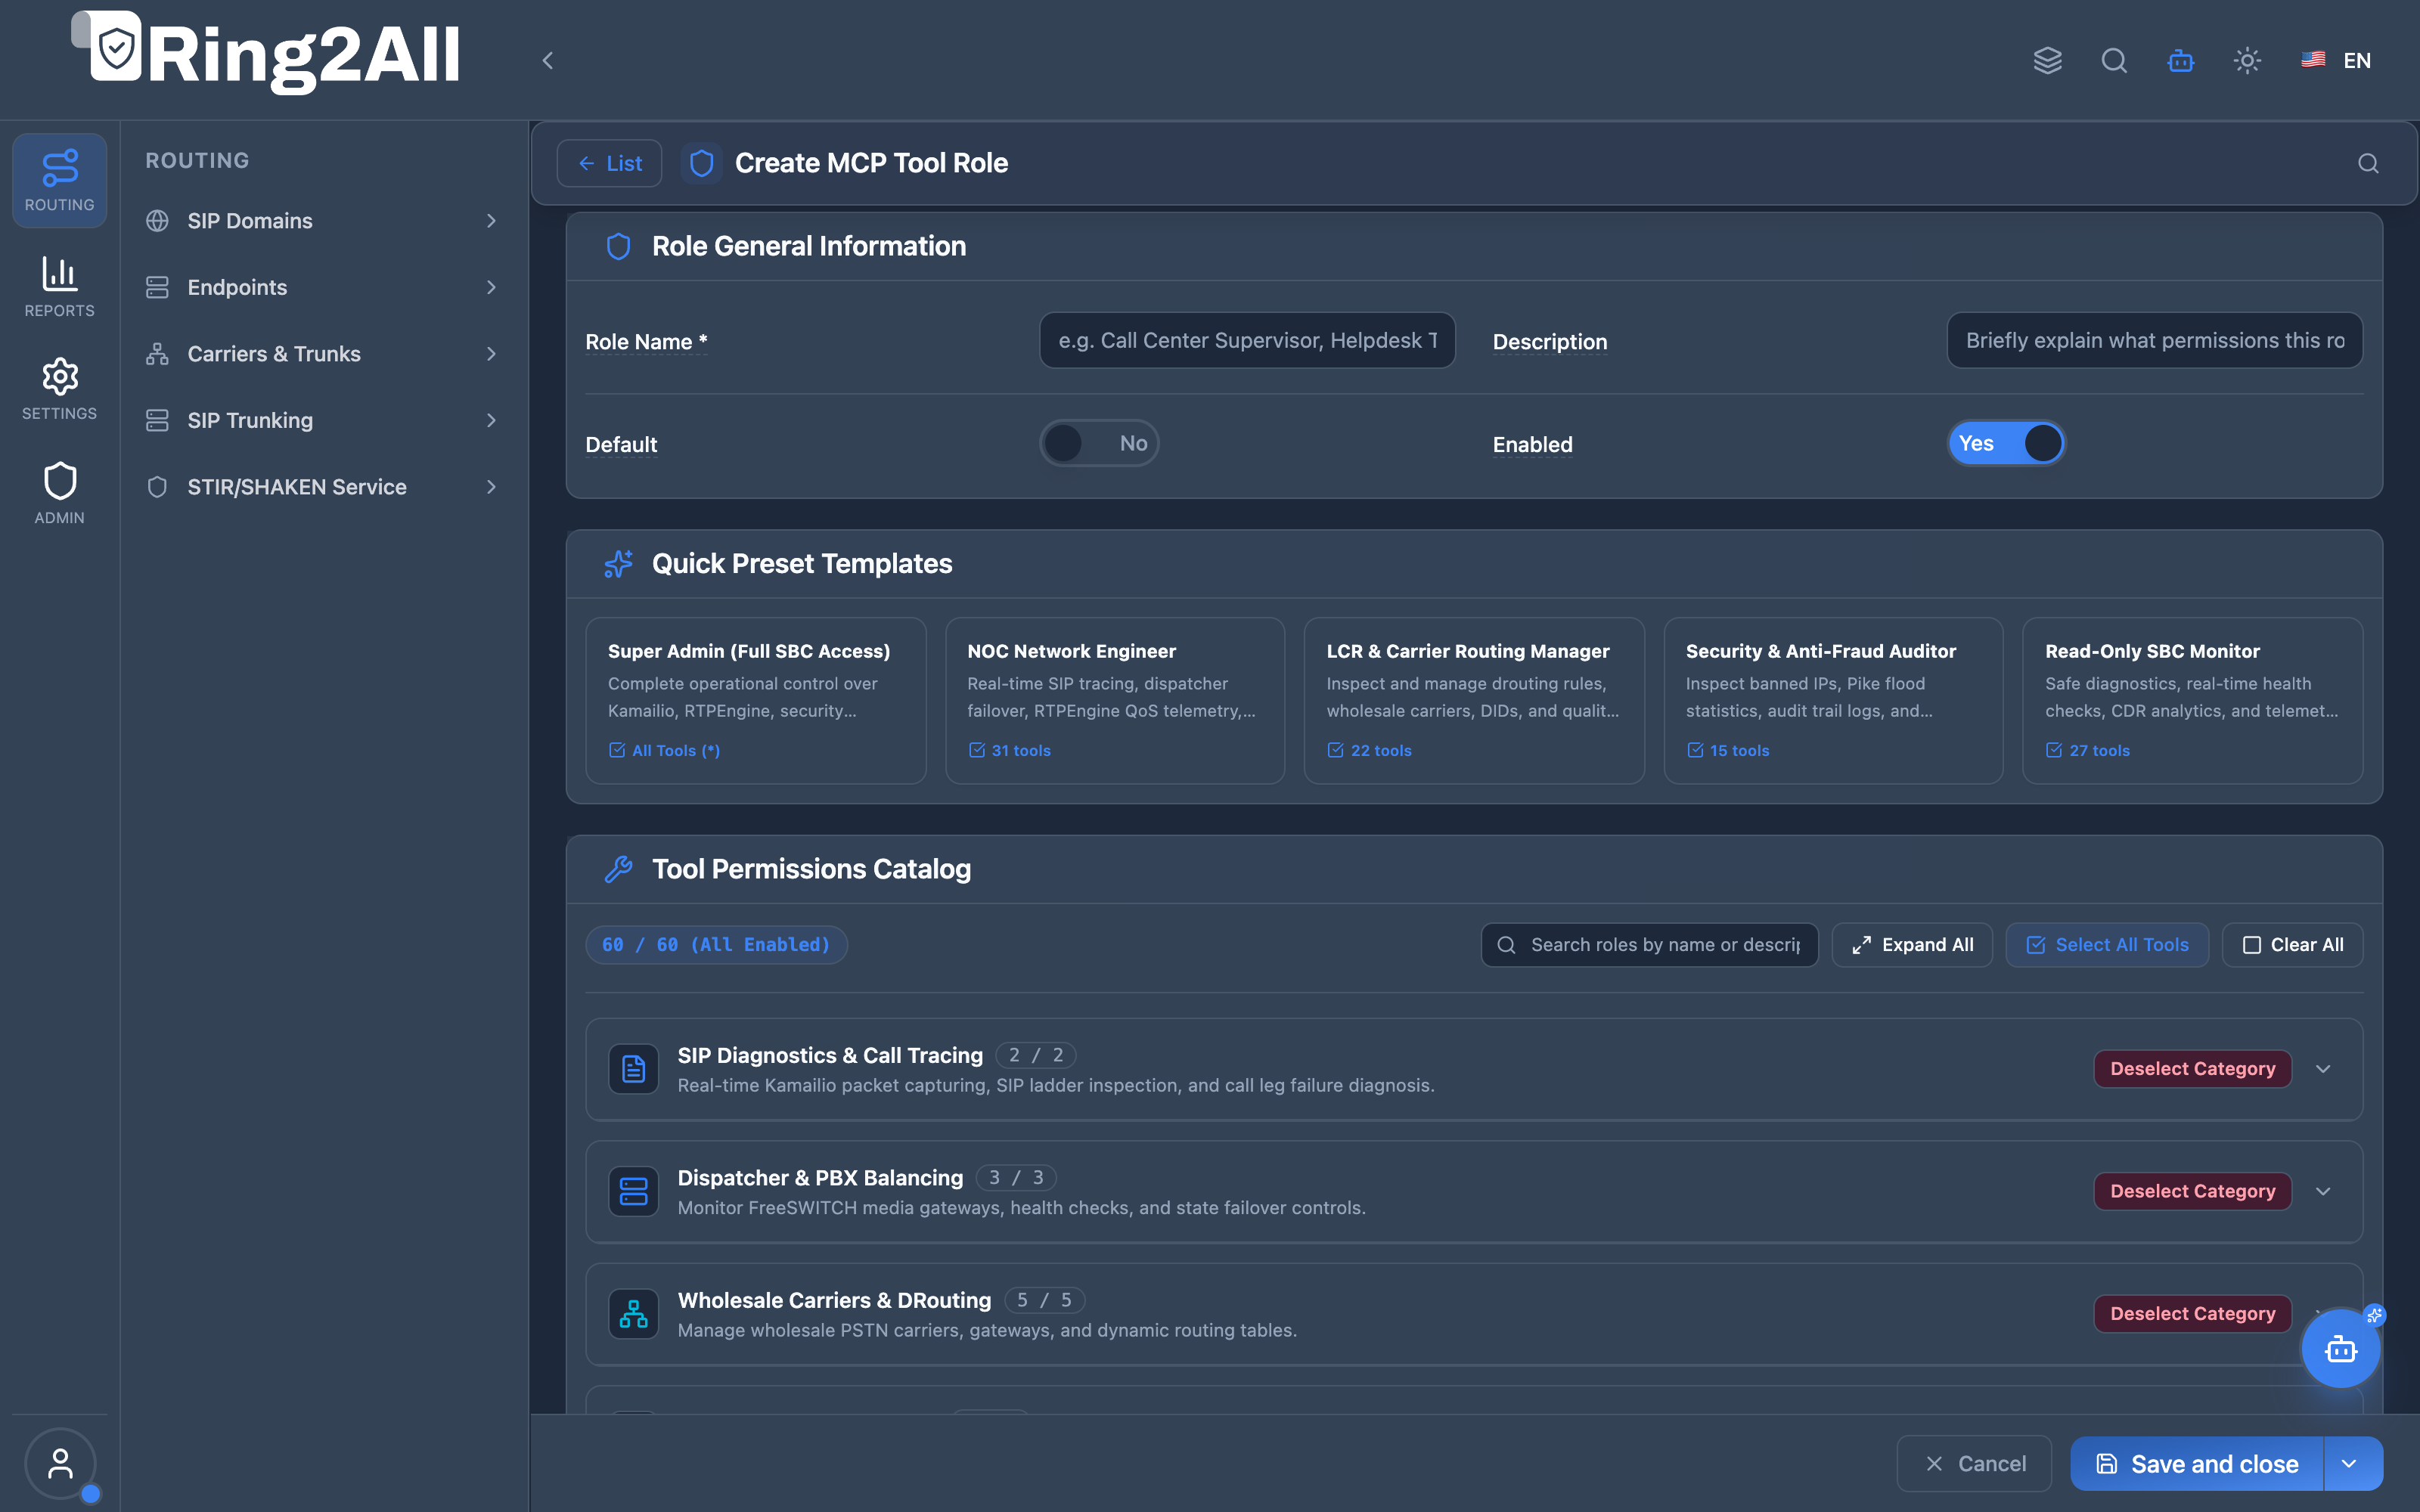
The MCP Role Profiles interface displays all registered AI tool profiles, their allowed tool counts, active statuses, and an interactive tool selection modal for role provisioning.
Displays existing AI tool profiles, assigned tools, default indicators, and management action buttons.
Modal editor providing tool group selectors, individual tool checkboxes, name, description, and status toggles.
Parameter Name
Data Type
Options / Format
Description
Role Name String
Alphanumeric (e.g., NOC Network Engineer)
Descriptive identifier indicating organizational AI responsibility.
Description Text
Text string
Operational purpose and scope of tool clearance.
Quick Presets Selector
Super Admin, NOC Engineer, Carrier Mgr, Security Auditor, MonitorPrepopulated tool bundles for rapid provisioning without individual checkbox selection.
Allowed Tools Array / Set
Tool names or * wildcard
Exhaustive array of permitted MCP tools for this profile.
Default Profile Switch
Boolean (true / false)
Automatically assigned to newly onboarded users if not explicitly specified.
Active Status Switch
Boolean (true / false)
Toggle to immediately suspend AI access for all accounts bound to this role profile.
Ring2All SBC provides a comprehensive suite of enterprise-grade MCP tools organized into functional subsystems, enabling autonomous diagnostics, full lifecycle CRUD configuration, and automated remediation:
Tool Identifier
Access Level
Description & Operational Impact
get_sip_tracesRead-Only
Queries live SIP transaction traces and extracts packet headers for a specified Call-ID.
explain_sip_callRead-Only
Synthesizes SIP trace ladders into human-readable fault explanations and identifies root cause error codes.
capture_and_analyze_sip_traceDiagnostic
Captures signaling packets for an active call and provides comprehensive timeline analysis.
diagnose_sip_error_spikesDiagnostic
Scans live SIP traces in real time for surges of 4xx/5xx/6xx error responses, calculates error rates per carrier and caller, and automates triage for common signaling failures.
get_sip_trace_capture_statusRead-Only
Checks whether global SIP packet capture and tracing is currently active in the SIP Engine.
set_sip_trace_capture_statusState-Modifying
Enables or disables real-time SIP signaling capture in the tracing subsystem.
Tool Identifier
Access Level
Description & Operational Impact
get_dispatcher_statusRead-Only
Checks the availability, latency, and status (Active/Probing/Inactive) of carrier trunks.
diagnose_dispatcherDiagnostic
Evaluates round-robin health, latency statistics, and socket states for a dispatcher node.
create_dispatcherState-Modifying
Adds a new SIP destination node to an existing dispatcher load-balancing set.
update_dispatcherState-Modifying
Modifies destination URI, capacity weight, flags, or priority for a dispatcher node.
delete_dispatcherState-Modifying
Removes a gateway node from a dispatcher group.
set_dispatcher_stateState-Modifying
Manually enables, disables, or places a carrier gateway into probing mode.
reload_dispatchersState-Modifying
Executes live reload of carrier gateways from PostgreSQL into SIP Engine memory without dropping calls.
Tool Identifier
Access Level
Description & Operational Impact
list_carriersRead-Only
Dumps carrier routing groups, assigned gateways, and cost tiers.
get_carrier_statusRead-Only
Inspects live connection state, active channels, and health status for a specific carrier.
diagnose_carrierDiagnostic
Evaluates carrier availability, recent failure rates, response times, and LCR participation.
create_carrierState-Modifying
Provisions a new upstream wholesale carrier gateway pool with routing parameters.
update_carrierState-Modifying
Updates carrier IP, port, protocol, concurrency limits, or operational state.
delete_carrierState-Modifying
Deletes a carrier trunk from the SBC routing system.
get_carrier_quality_metricsRead-Only
Compiles ASR, ACD, and PDD performance metrics for a specific carrier trunk.
Tool Identifier
Access Level
Description & Operational Impact
list_lcr_routesRead-Only
Evaluates prefix trees to explain which carrier trunk will be chosen for a given dialed number.
get_lcr_route_statusRead-Only
Inspects active route status, priority sequence, and gateway lists for an LCR rule.
diagnose_lcr_routeDiagnostic
Simulates digit normalization, prefix matching, and gateway failover sequences for a dial pattern.
create_lcr_routeState-Modifying
Defines a new dynamic routing rule with prefix patterns and ordered carrier gateways.
update_lcr_routeState-Modifying
Modifies route priority, destination prefix, or assigned carrier gateway groups.
delete_lcr_routeState-Modifying
Removes an LCR route rule from the dynamic routing matrix.
reload_drouting_rulesState-Modifying
Reloads dynamic routing rules and LCR prefix trees in shared memory without service interruption.
Tool Identifier
Access Level
Description & Operational Impact
list_didsRead-Only
Lists inbound Direct Inward Dialing (DID) numbers, routing destinations, and tenant mappings.
get_did_statusRead-Only
Inspects configuration and routing status for a specific DID number.
diagnose_didDiagnostic
Simulates inbound translation, header manipulation, and endpoint matching for an incoming DID.
create_didState-Modifying
Adds a new inbound DID number with destination translation rules.
update_didState-Modifying
Updates routing destination, tenant assignment, or fallback handling for a DID.
delete_didState-Modifying
Removes a DID translation record from the SBC database.
Tool Identifier
Access Level
Description & Operational Impact
list_sbc_endpointsRead-Only
Lists internal PBX core nodes and cluster dispatch destinations.
create_sbc_endpointState-Modifying
Registers a new PBX core cluster node in the SBC routing table.
update_sbc_endpointState-Modifying
Modifies host IP, port, weight, or active status for a PBX endpoint.
delete_sbc_endpointState-Modifying
Removes a PBX core node from the SBC ingress pool.
Tool Identifier
Access Level
Description & Operational Impact
list_sip_domainsRead-Only
Lists all multi-tenant SIP domains managed by the SBC perimeter.
get_sip_domain_statusRead-Only
Inspects domain routing group and active registration status.
diagnose_sip_domainDiagnostic
Validates DNS SRV resolution, TLS certificate matching, and dispatcher mapping for a domain.
create_sip_domainState-Modifying
Provisions a new multi-tenant SIP domain on the SBC.
update_sip_domainState-Modifying
Modifies domain parameters, default routing set, or security policy.
delete_sip_domainState-Modifying
Removes a SIP domain from the active perimeter database.
reload_sip_domainsState-Modifying
Triggers instant in-memory reload of domain routing tables in the SIP Engine.
Tool Identifier
Access Level
Description & Operational Impact
list_smr_rulesRead-Only
Lists header transformation and packet manipulation rules.
get_smr_rule_statusRead-Only
Inspects matching criteria and transformation actions of an SMR rule.
diagnose_smr_ruleDiagnostic
Tests header regex substitutions, URI rewriting, and condition evaluations on sample SIP messages.
create_smr_ruleState-Modifying
Creates a new SIP message manipulation rule (e.g., stripping privacy headers, rewriting From URI).
update_smr_ruleState-Modifying
Updates match conditions, regex expressions, or replacement actions for an SMR rule.
delete_smr_ruleState-Modifying
Removes a message manipulation rule from the processing pipeline.
Tool Identifier
Access Level
Description & Operational Impact
list_trusted_ipsRead-Only
Lists trusted IP addresses and CIDR subnets exempt from Digest authentication.
diagnose_acl_permissionDiagnostic
Verifies IP authorization, subnet matching, and permission group membership for a remote host.
add_trusted_ipState-Modifying
Authorizes a new trusted IP address or CIDR range in the perimeter access control table.
remove_trusted_ipState-Modifying
Revokes trusted status from an IP address or subnet.
reload_acl_permissionsState-Modifying
Executes instant reload of permissions tables in the SIP Engine.
Tool Identifier
Access Level
Description & Operational Impact
list_sip_accountsRead-Only
Lists subscriber SIP accounts, authentication methods, and capacity limits.
get_sip_account_statusRead-Only
Inspects registration state, contact bindings, and concurrency counters for an account.
diagnose_sip_accountDiagnostic
Verifies Digest credentials, HA1 hash integrity, registration timers, and ACL matching.
create_sip_accountState-Modifying
Creates a new subscriber account with Digest credentials and channel limits.
update_sip_accountState-Modifying
Modifies SIP credentials, authentication realm, or channel caps.
delete_sip_accountState-Modifying
Removes a subscriber SIP account from the SBC.
Tool Identifier
Access Level
Description & Operational Impact
list_msteams_tenantsRead-Only
Lists configured Microsoft Teams customer tenants and SIP trunks.
get_msteams_statusRead-Only
Inspects TLS handshake state and OPTIONS keepalive telemetry with Microsoft PSTN gateways.
diagnose_msteamsDiagnostic
Diagnoses mutual TLS authentication, domain verification, and Microsoft OPTIONS responses.
create_msteams_tenantState-Modifying
Provisions a new Microsoft Teams customer tenant with Direct Routing parameters.
update_msteams_tenantState-Modifying
Modifies tenant FQDN, TLS profile, or domain routing parameters.
delete_msteams_tenantState-Modifying
Removes a Microsoft Teams tenant configuration.
Tool Identifier
Access Level
Description & Operational Impact
diagnose_webrtcDiagnostic
Verifies Secure WebSocket (WSS) listeners, DTLS-SRTP certificates, and ICE/STUN/TURN relay readiness.
Tool Identifier
Access Level
Description & Operational Impact
get_rtpengine_statusRead-Only
Retrieves Media Relay daemon health, active media sessions, and port pool utilization.
diagnose_media_relayDiagnostic
Checks control socket responsiveness, active audio streams, and kernel-space relay telemetry.
get_voice_qos_telemetryRead-Only
Extracts real-time jitter, packet loss percentage, round-trip delay, and MOS score across active streams.
analyze_call_qos_streamDiagnostic
Performs forensic quality analysis on an active or finished call, isolating latency spikes and jitter bursts.
diagnose_one_way_audioDiagnostic
Analyzes call CDRs and SIP trace SDP offer/answer messages to detect one-way audio streams, asymmetric packet loss, extreme jitter, and NAT IP mismatches.
get_qos_alert_policyRead-Only
Queries active voice quality alarm thresholds and automated notification rules.
update_qos_alert_policyState-Modifying
Configures MOS drop thresholds, packet loss trigger levels, and alert recipient lists.
Tool Identifier
Access Level
Description & Operational Impact
get_banned_ipsRead-Only
Queries the perimeter memory hash table to list all IP addresses currently blocked by Pike anti-flood.
ban_ip_addressState-Modifying
Immediately blocks a hostile IP address in the perimeter firewall and memory tables.
unban_ip_addressState-Modifying
Purges an IP address from memory hash tables and unblocks it in the firewall to restore service.
diagnose_perimeter_securityDiagnostic
Analyzes packet drop rates, Pike offenders, active kernel bans, and geo-firewall hit rates.
Tool Identifier
Access Level
Description & Operational Impact
sbc_get_threat_intelligence_summaryRead-Only
Retrieves real-time security posture, total banned hosts, active threats, and attack distribution.
sbc_analyze_ip_securityDiagnostic
Computes threat risk scores, behavioral anomalies, and IRSF patterns for a target IP address.
sbc_list_security_incidentsRead-Only
Lists recent security events, brute-force attempts, header anomalies, and automated mitigations.
sbc_mitigate_threat_ipState-Modifying
Executes autonomous threat containment and applies immediate kernel ban rules against malicious hosts.
Tool Identifier
Access Level
Description & Operational Impact
get_stirshaken_configRead-Only
Inspects STIR/SHAKEN signing and verification configuration, certificate paths, and attestation defaults.
update_stirshaken_configState-Modifying
Updates attestation levels (A, B, C), certificate store paths, or verification policy.
verify_caller_identityDiagnostic
Simulates PASSporT token validation and cryptographic verification for a specified caller number.
Tool Identifier
Access Level
Description & Operational Impact
analyze_server_healthRead-Only
Deep server hardware, OS distribution, CPU/RAM/Swap load, storage partition capacity, database latency, and system engine telemetry.
get_sbc_healthRead-Only
Retrieves CPU load, memory utilization, process health, and database connection pools.
get_sbc_audit_logsRead-Only
Inspects administrative audit trails, user actions, and system mutation records.
log_sbc_audit_eventState-Modifying
Records an administrative or autonomous compliance event in the audit trail.
get_engine_settingsRead-Only
Inspects low-level SIP Engine parameters, memory allocations, and network socket bindings.
update_engine_settingsState-Modifying
Updates operational parameters in the core SIP Engine configuration.
get_billing_settingsRead-Only
Queries real-time CDR rating and billing engine integration configurations.
list_tls_profilesRead-Only
Lists configured TLS encryption profiles, cipher suites, and verification modes.
get_tls_profile_statusRead-Only
Inspects validity, cipher settings, and handshake statistics for a TLS profile.
reload_tls_profilesState-Modifying
Reloads TLS certificates and cryptographic contexts in the SIP Engine without dropping connections.
list_mtreesRead-Only
Lists memory trees (mtrees) used for high-speed prefix matching and LCR.
reload_mtreesState-Modifying
Reloads memory tree prefix structures in shared memory.
list_htablesRead-Only
Inspects in-memory hash tables used for caching, rate limiting, and ban tracking.
get_htable_entriesRead-Only
Dumps entries from a specific in-memory hash table.
reload_htablesState-Modifying
Reloads hash table configurations from the database.
execute_rpc_commandRestricted
Executes a sanitized management RPC command on the SIP Engine with strict parameter validation.
get_rpc_suggestionsRead-Only
Provides syntax suggestions and parameter descriptions for management RPC commands.
list_sbc_usersRead-Only
Lists administrative user accounts and assigned permission roles.
get_sbc_userRead-Only
Retrieves detailed profile and clearance information for an administrative user.
list_sbc_role_profilesRead-Only
Lists RBAC role profiles defined on the SBC with assigned user counts.
get_sbc_role_profileRead-Only
Retrieves detailed module permissions for an RBAC role profile.
list_sbc_mcp_rolesRead-Only
Lists all AI Copilot MCP tool roles with total allowed tool counts and assigned operators.
get_sbc_mcp_roleRead-Only
Retrieves detailed tool whitelist and category clearance for a specific MCP role.
Ring2All SBC provides five official pre-configured AI governance profiles:
Scope : Wildcard (["*"])Purpose : Full autonomous access to all diagnostic, analytical, CRUD provisioning, and state-modifying tools. Reserved exclusively for senior infrastructure engineers and platform administrators.
Scope : Advanced Diagnostics + Active Remediation + State ModificationCapabilities : Comprehensive SIP tracing, packet ladder forensics, dispatcher failover, carrier health diagnosis, Media Relay inspection, voice QoS analysis, and perimeter IP unbanning.Key Tools : get_sip_traces, explain_sip_call, capture_and_analyze_sip_trace, get_dispatcher_status, diagnose_dispatcher, set_dispatcher_state, reload_dispatchers, list_carriers, get_carrier_status, diagnose_carrier, list_lcr_routes, get_lcr_route_status, diagnose_lcr_route, reload_drouting_rules, get_rtpengine_status, diagnose_media_relay, get_voice_qos_telemetry, analyze_call_qos_stream, get_banned_ips, unban_ip_address, ban_ip_address, diagnose_perimeter_security, get_sbc_health, analyze_server_health.
Scope : Carrier Lifecycle, Routing Matrices, Prefix Trees & Inbound DIDsCapabilities : Full CRUD provisioning of wholesale carriers, dynamic LCR routes, prefix tables, inbound DIDs, PBX endpoints, and traffic analytics inspection.Key Tools : list_carriers, get_carrier_status, diagnose_carrier, create_carrier, update_carrier, delete_carrier, list_lcr_routes, get_lcr_route_status, diagnose_lcr_route, create_lcr_route, update_lcr_route, delete_lcr_route, reload_drouting_rules, list_dids, get_did_status, diagnose_did, create_did, update_did, delete_did, list_sbc_endpoints, create_sbc_endpoint, update_sbc_endpoint, delete_sbc_endpoint, get_carrier_quality_metrics, get_traffic_analytics, get_top_destinations, get_sbc_cdrs.
Scope : Host Defense, Anti-Flood, ACL Lists, STIR/SHAKEN & Forensic LogsCapabilities : Management of Pike anti-flood hash tables, trusted IP access lists, threat intelligence scoring, STIR/SHAKEN identity verification, and administrative audit inspection.Key Tools : get_banned_ips, ban_ip_address, unban_ip_address, diagnose_perimeter_security, list_trusted_ips, add_trusted_ip, remove_trusted_ip, diagnose_acl_permission, reload_acl_permissions, sbc_get_threat_intelligence_summary, sbc_analyze_ip_security, sbc_list_security_incidents, sbc_mitigate_threat_ip, get_stirshaken_config, update_stirshaken_config, verify_caller_identity, get_sbc_audit_logs, log_sbc_audit_event, get_sbc_health, analyze_server_health.
Scope : Strictly View-Only TelemetryCapabilities : Real-time observability across active calls, SIP traces, voice QoS metrics, carrier availability, and cluster health without permission to alter running daemons or database records.Key Tools : explain_sip_call, get_sip_traces, get_sip_trace_capture_status, get_dispatcher_status, diagnose_dispatcher, list_carriers, get_carrier_status, diagnose_carrier, list_lcr_routes, get_lcr_route_status, diagnose_lcr_route, list_dids, get_did_status, diagnose_did, list_sbc_endpoints, list_sip_domains, get_sip_domain_status, diagnose_sip_domain, get_rtpengine_status, diagnose_media_relay, get_voice_qos_telemetry, analyze_call_qos_stream, get_banned_ips, diagnose_perimeter_security, diagnose_webrtc, sbc_get_threat_intelligence_summary, get_sbc_health, analyze_server_health, get_traffic_analytics, get_top_destinations.
When the AI model determines that a tool should be executed, the request passes through the MCP Tool Authorization Guard :
export async function assertUserCanExecuteTool (
. selectFrom ( ' users as u ' )
. leftJoin ( ' mcp_roles as r ' , ' r.id ' , ' u.mcp_role_id ' )
. select ([ ' r.allowed_tools as allowedTools ' , ' r.is_active as isActive ' ])
. where ( ' u.id ' , ' = ' , userId)
if ( ! user || ! user . isActive ) {
throw new ForbiddenError ( ' User has no active MCP Tool Role assigned ' );
const tools : string [] = typeof user . allowedTools === ' string '
? JSON . parse (user . allowedTools )
: (user . allowedTools || []);
// Super Admin wildcard or explicit tool match
if (tools . includes ( ' * ' ) || tools . includes (toolName)) {
return ; // Authorized to execute
throw new ForbiddenError ( ` MCP tool ' ${ toolName } ' is not permitted for the user's role ` );
Verify configured AI tool permissions directly on the SBC:
sudo -u postgres psql -d sbc_admin -c "
SELECT id, name, is_system, allowed_tools
Inspect security audit logs for unauthorized AI tool attempts:
sudo -u postgres psql -d sbc_admin -c "
SELECT created_at, user_id, action, details
WHERE action LIKE '%mcp_tool_denied%'
Ring2All SBC exposes dedicated Model Context Protocol (MCP) governance tools enabling AI agents to inspect MCP role configurations, verify tool whitelists, and perform self-introspection on permitted boundaries.
Tool Name
Operation
Risk Level
Description
list_sbc_mcp_rolesRead
Low (read)
List all AI Copilot MCP tool roles with total allowed tool counts, default flags, and assigned operator counts.
get_sbc_mcp_roleRead
Low (read)
Retrieve the detailed tool whitelist and category clearance for a specific MCP role by UUID, slug, or ID.
"name" : " list_sbc_mcp_roles " ,
"description" : " List Model Context Protocol (MCP) AI Tool RBAC roles in Ring2All SBC with permitted tool counts and assigned users. " ,
"name" : " get_sbc_mcp_role " ,
"description" : " Get detailed MCP tool whitelist and permissions for a specific MCP role by UUID, slug, or ID. " ,
"description" : " MCP role UUID, slug, or numeric ID "
"required" : [ " identifier " ]
"identifier" : " noc_network_engineer "
"uuid" : " 8e14f092-23c1-4ba2-b5e0-47120aef8912 " ,
"name" : " NOC Network Engineer " ,
"slug" : " noc_network_engineer " ,
"description" : " Perimeter network diagnostics, SIP traces ladder inspection, Media Relay QoS telemetry, dispatcher state management, and real-time firewall mitigation. " ,
" capture_and_analyze_sip_trace " ,
" get_voice_qos_telemetry " ,
" analyze_call_qos_stream " ,
" diagnose_perimeter_security " ,
" get_sbc_email_alarm_settings "
"created_at" : " 2026-01-15T08:00:00Z " ,
"updated_at" : " 2026-09-08T11:00:00Z "
“Check which MCP tools are allowed for my active role profile and confirm if I have permission to unban an IP address or reload SIP Engine dispatchers.”
“Lista todos los perfiles de herramientas MCP disponibles en el SBC y muestra cuántos operadores tienen asignado el perfil con acceso completo (‘super_admin’).”
Self-Contained Role Introspection : AI models can query their assigned tool whitelist to gracefully explain permission boundaries to human operators without triggering runtime 403 errors.Wildcard Execution Containment : The super_admin wildcard (*) is restricted strictly to accounts verified with root administrative credentials.
MCP (Model Context Protocol) : An open standard created by Anthropic that enables AI assistants to securely discover and invoke tools, data sources, and APIs.NOC Copilot : Ring2All SBC’s specialized conversational AI assistant fine-tuned for telecom troubleshooting and SIP diagnostics.Tool Call : A structured JSON object generated by an LLM requesting the host application to run a specific function with provided arguments.Prompt Injection : A cybersecurity vulnerability where an attacker manipulates an AI model’s instructions through crafted text inputs.